Module 05
Live Ingest Server & Stream Hijack Security
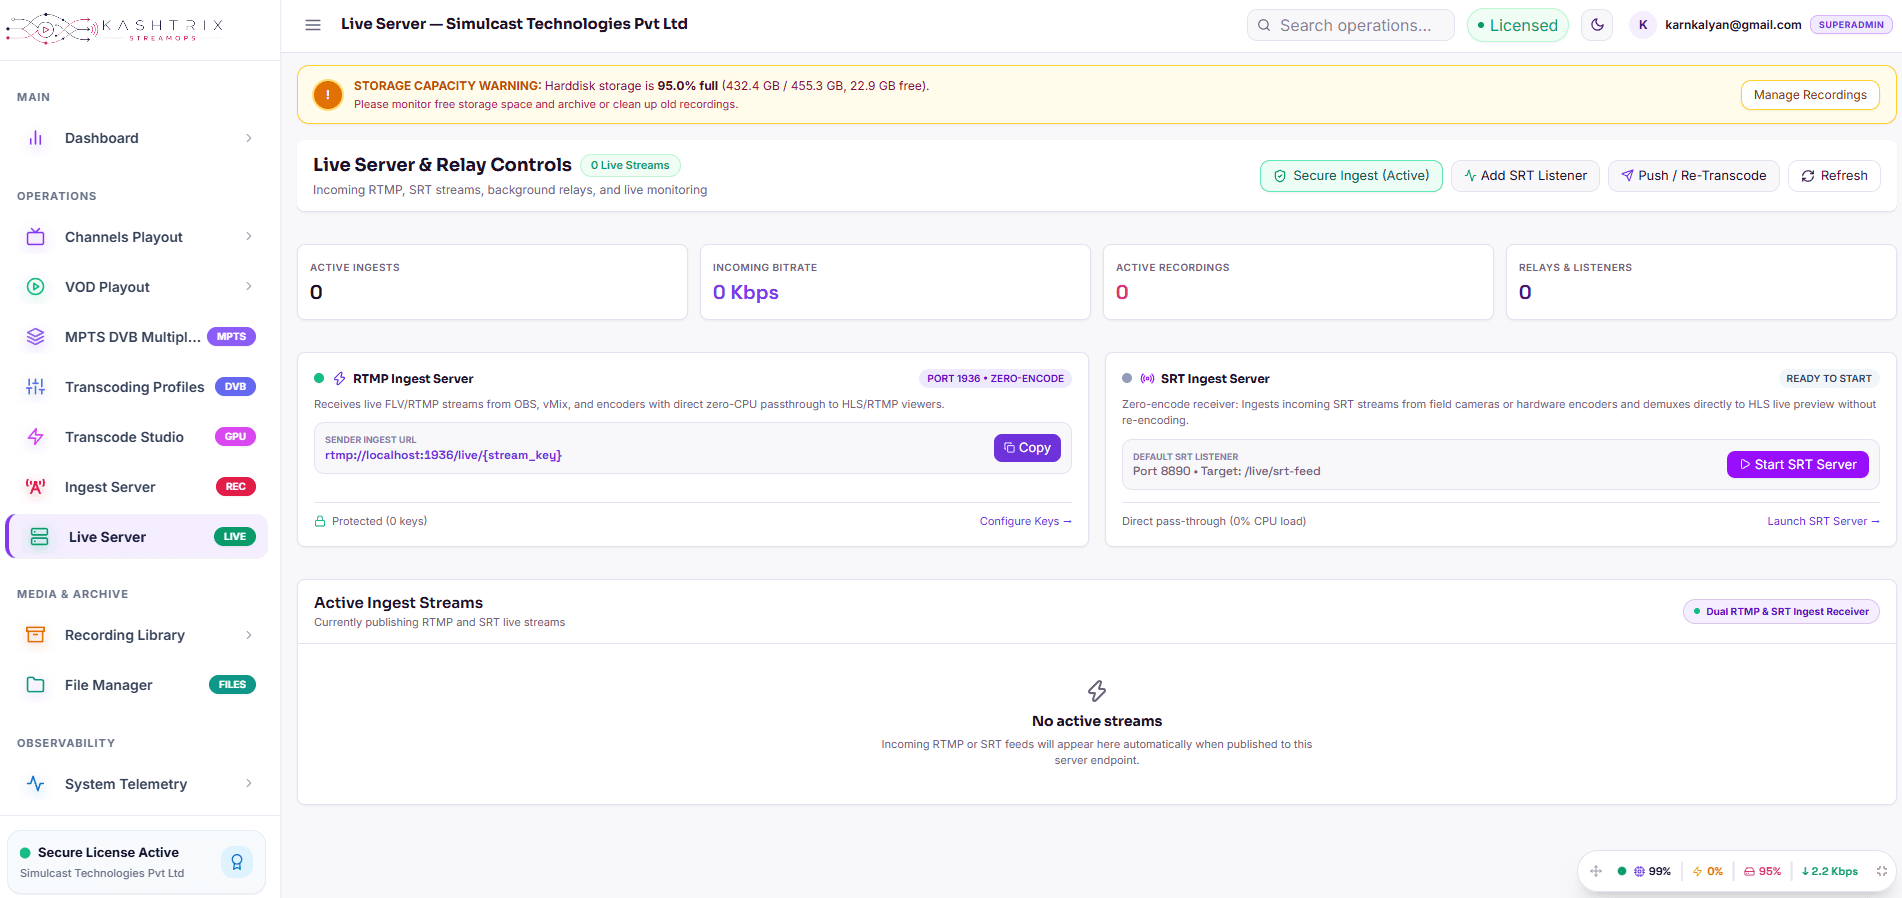
Hardened RTMP/RTMPS and SRT ingest gateway designed to prevent unauthorized broadcast access and stream piracy.
Operational scope
Purpose-built for this media task.
The module remains part of the StreamOps control plane, but the page and visual treatment follow the actual workflow rather than a repeated template.
Dual security enforcement modes: toggle between Open (studio staging) and Protected (production enforcement) modes
Multi-factor publisher authentication: URL stream key (?key=... / ?token=...), username/password credentials and stream path whitelisting
Single-publisher concurrency lock: strict anti-hijacking prevention ensuring duplicate publishers cannot transmit on an active key
Live session telemetry: monitor publisher IP, protocol, incoming bitrate, jitter, frame rate and duration with one-click disconnect & IP ban
Broadcast-native
Built around signal paths, protocols and operational state.
Governed
Roles and audit controls stay attached to actions.
Observable
System state remains visible across related modules.
Next StreamOps module
External Studio Automation & TCP Control Protocol
Integrate StreamOps with broadcast television studio automation, vision switchers and physical controllers via low-latency TCP socket protocol (Port 9999).
StreamOps engineering
Deploy Live Ingest Server & Stream Hijack Security in your media path.
Share the sources, protocols, hardware, bitrate targets and operating model. We’ll align the StreamOps configuration to the workflow.