Platform security
Protect access. Preserve operational trust.
Apply identity, permissions, auditability and controlled automation across telecom workflows and integrations.
Identity-led
Policy-aware
Auditable
Defense-in-depth
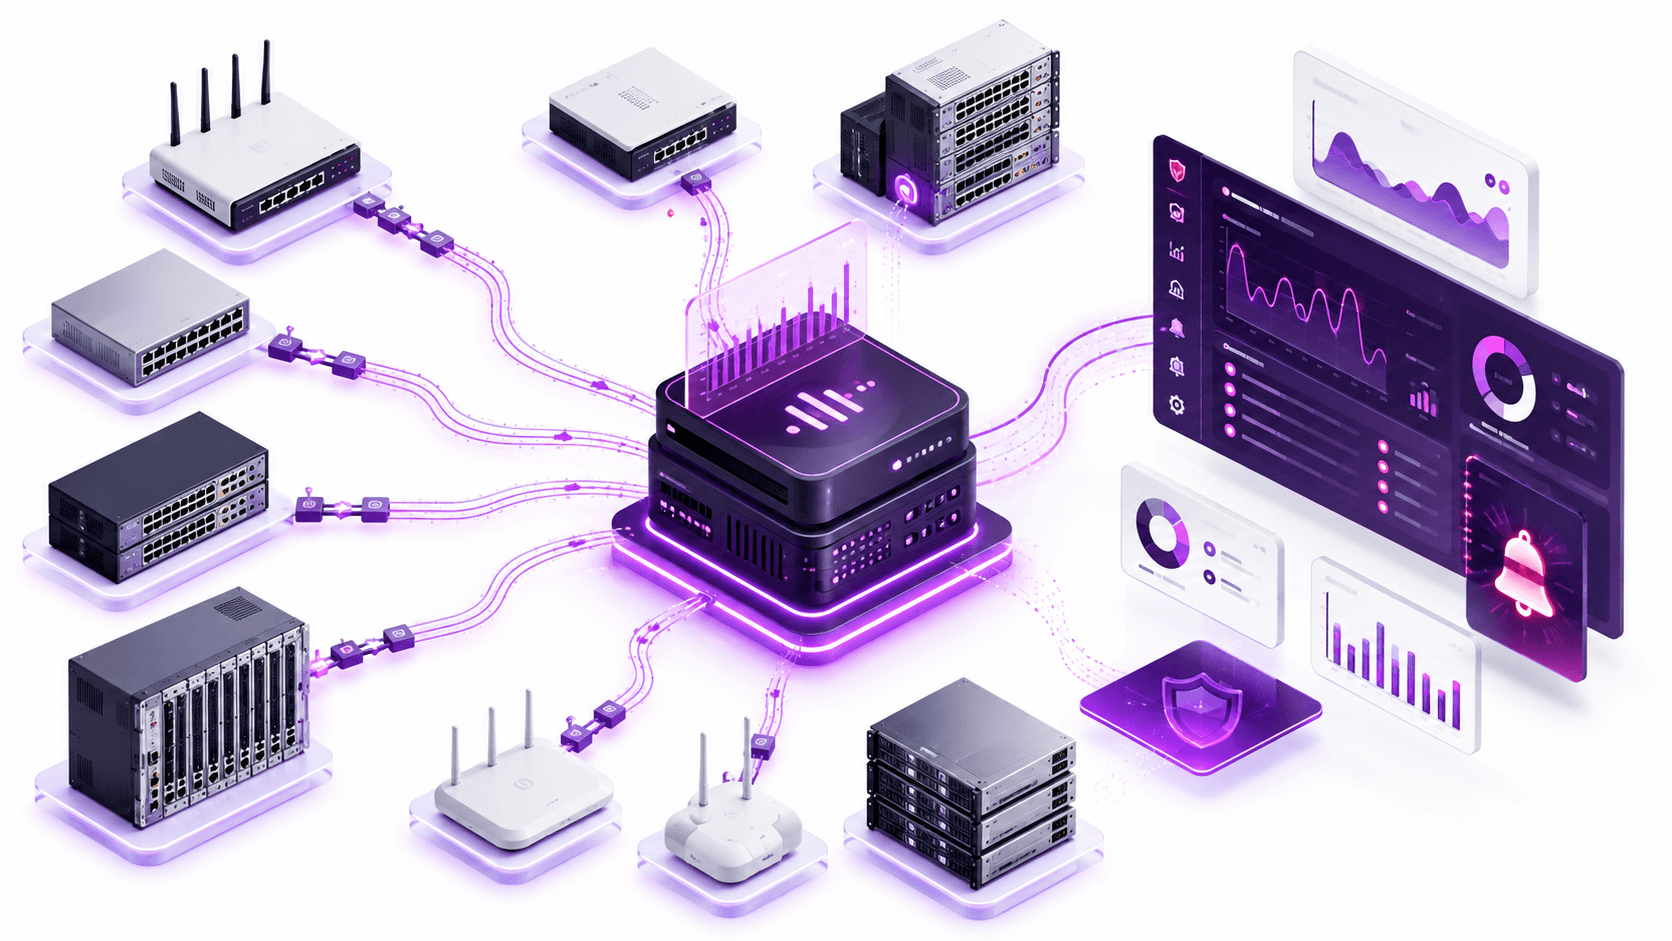
System scope
The capabilities operators use to move work forward.
The OSS/BSS pages use the same Kashtrix visual language, but each domain changes layout, emphasis and information density to match its operational role.
Access controls
Apply scoped roles and permissions around operational capabilities.
Audit evidence
Maintain traceable records of sensitive changes and actions.
Integration security
Protect credentials and connected service boundaries.
Operational guardrails
Put approvals and policy checks around automation.
Security visibility
Surface relevant activity and exceptions for review.
Operational workflow
A visible path from input to outcome.
The workflow below reflects this product domain rather than repeating a generic dashboard story.
Step 1
Authenticate actor
Policy, ownership and evidence remain attached to the work as it progresses.
Step 2
Evaluate policy
Policy, ownership and evidence remain attached to the work as it progresses.
Step 3
Authorize action
Policy, ownership and evidence remain attached to the work as it progresses.
Step 4
Record evidence
Policy, ownership and evidence remain attached to the work as it progresses.
Step 5
Review exceptions
Policy, ownership and evidence remain attached to the work as it progresses.
Controlled access
Roles and permissions around operational actions.
Traceable change
Keep intent and result visible for review.
Operational context
Bring relevant network or business state into the task.
Platform security deployment
Evaluate Protect access for your operation.
Share your subscriber scale, network vendors, AAA stack, billing model and automation requirements. We’ll map integrations and an implementation path.